KeyStealth: Device code phishing to rogue Entra devices and BEC
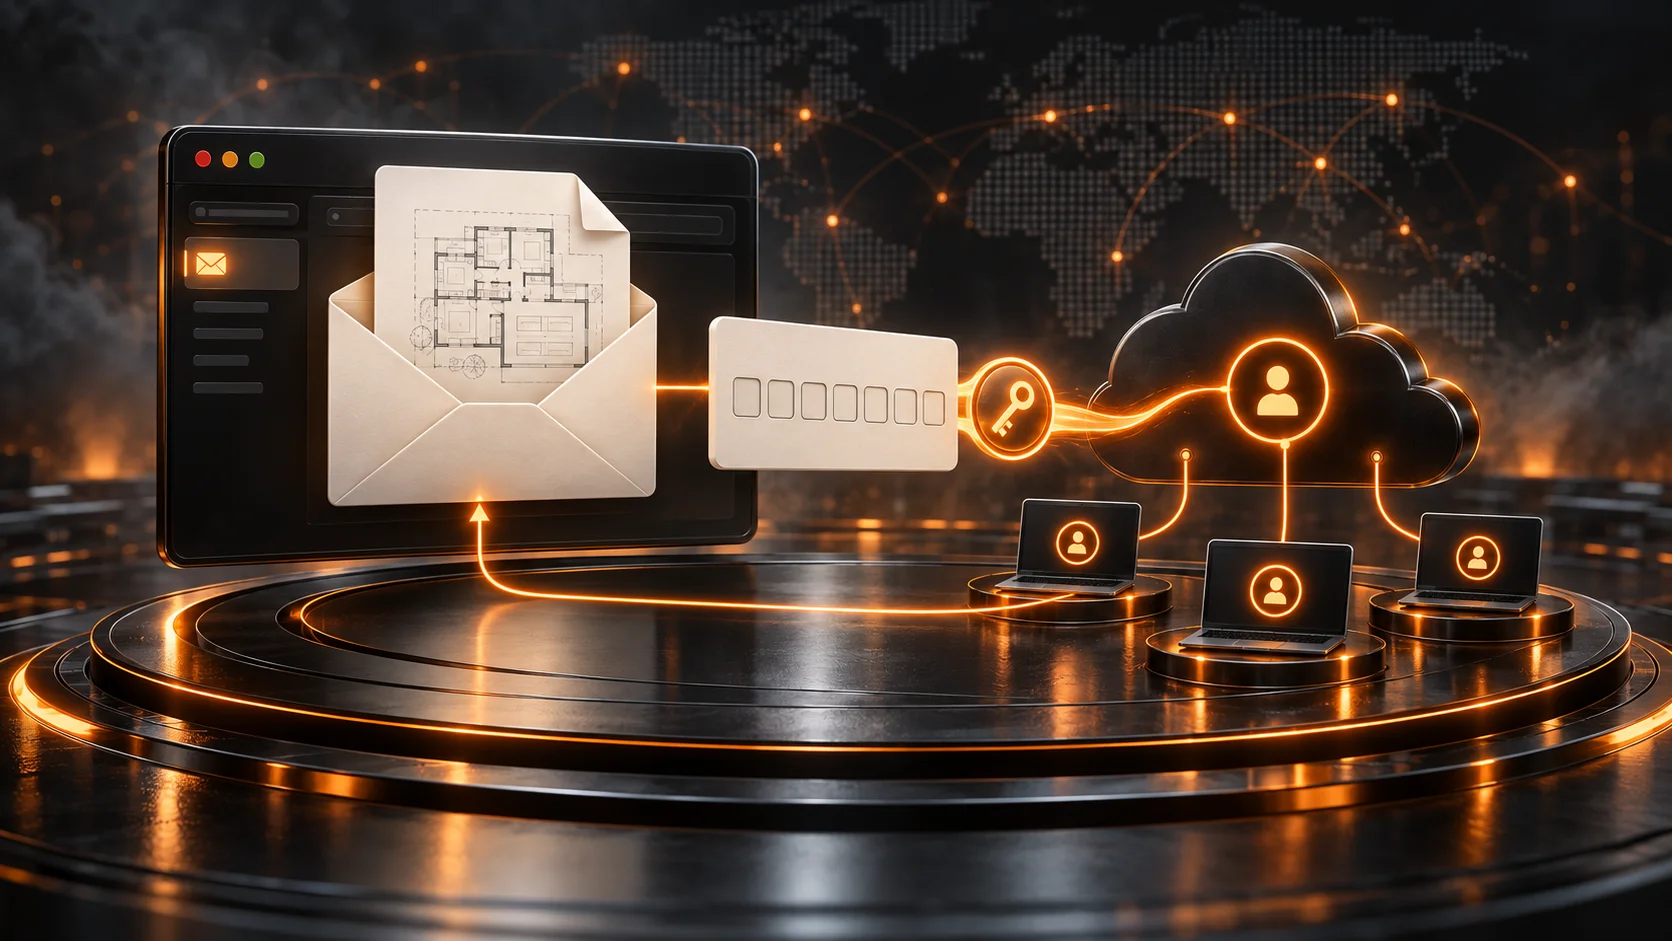
A construction quote lure led to device code phishing, three rogue Entra devices named iAuthFlow-Device, and seven weeks of mail access before a thread hijack.
Deep dives
Original technical analysis of active threats, vulnerable systems, and defensive architecture.
1–6 of 6
RSS
A construction quote lure led to device code phishing, three rogue Entra devices named iAuthFlow-Device, and seven weeks of mail access before a thread hijack.

Tax-themed ISOs sideload ValleyRAT through a signed Visual Studio tool. Five months of builds share one transport key and a text file that hands out new servers.

Two ClickFix kits fought over the same screen on hacked WordPress sites. One wrote the fight into its code, in Russian, down to the moment the browser broke.

Brevo served KongTuke ClickFix from its own infrastructure. Altered tracker scripts, forms, and unsubscribe pages delivered the attack to customer sites.

A compromised HBO Max Reddit account led to PasteSwitch, a cross-platform ClickFix operation spanning macOS stealers, Windows loaders, deceptive TLS, and contract-controlled clippers.

A 99 KB Mirai-derived sample scanned 238,756 hosts in 149 seconds. RondoDox shows how Zero Trust Connectivity can contain compromised IoT devices.